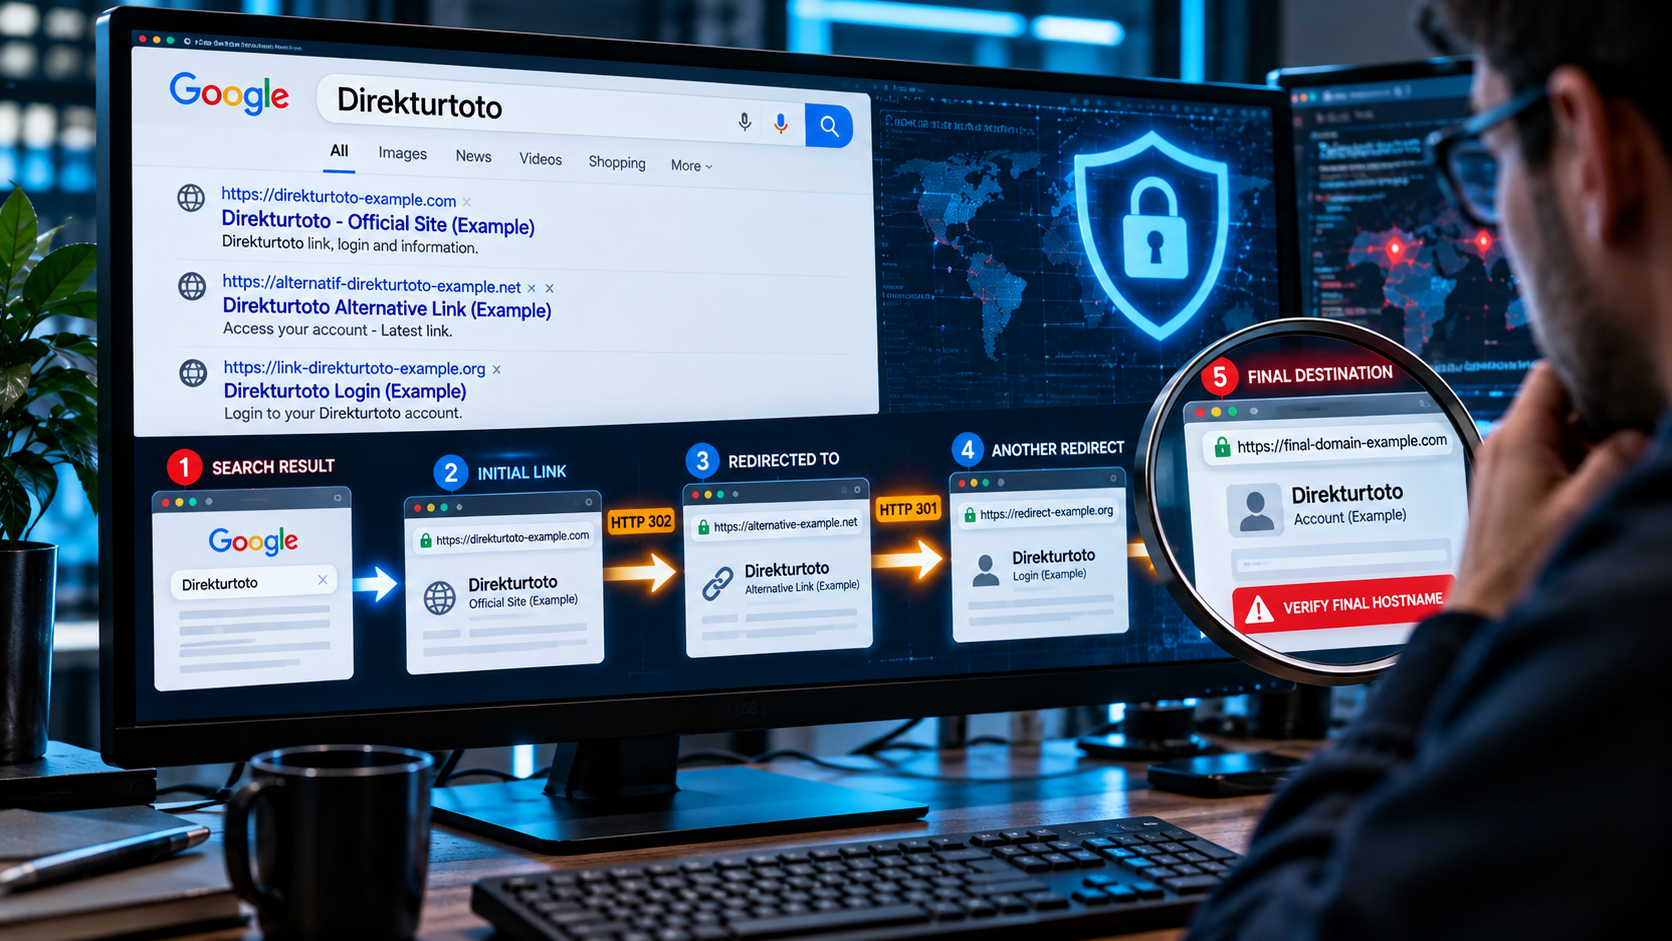
Searching for Direkturtoto can lead to more than a single straightforward website. Current search results include different domains, login-related pages, link aggregators and pages explicitly advertising “alternative” Direkturtoto links.
From a cybersecurity perspective, this creates a useful case study in redirect security.
The central question is not which Direkturtoto link should someone use. This article does not recommend a gambling platform or provide registration, betting or payment instructions.
Instead, the important security question is:
When a search result or alternative link sends you through one or more domains, how can you determine where your browser actually ends up before trusting the page?
That question applies far beyond Direkturtoto. Redirect chains, mirror domains and alternative URLs are common across the web, and they can be used legitimately. But similar mechanisms can also be abused for phishing, impersonation, malicious advertising and credential theft.
Understanding the difference starts with the browser address bar.
A user searching for a familiar name often focuses on the page title.
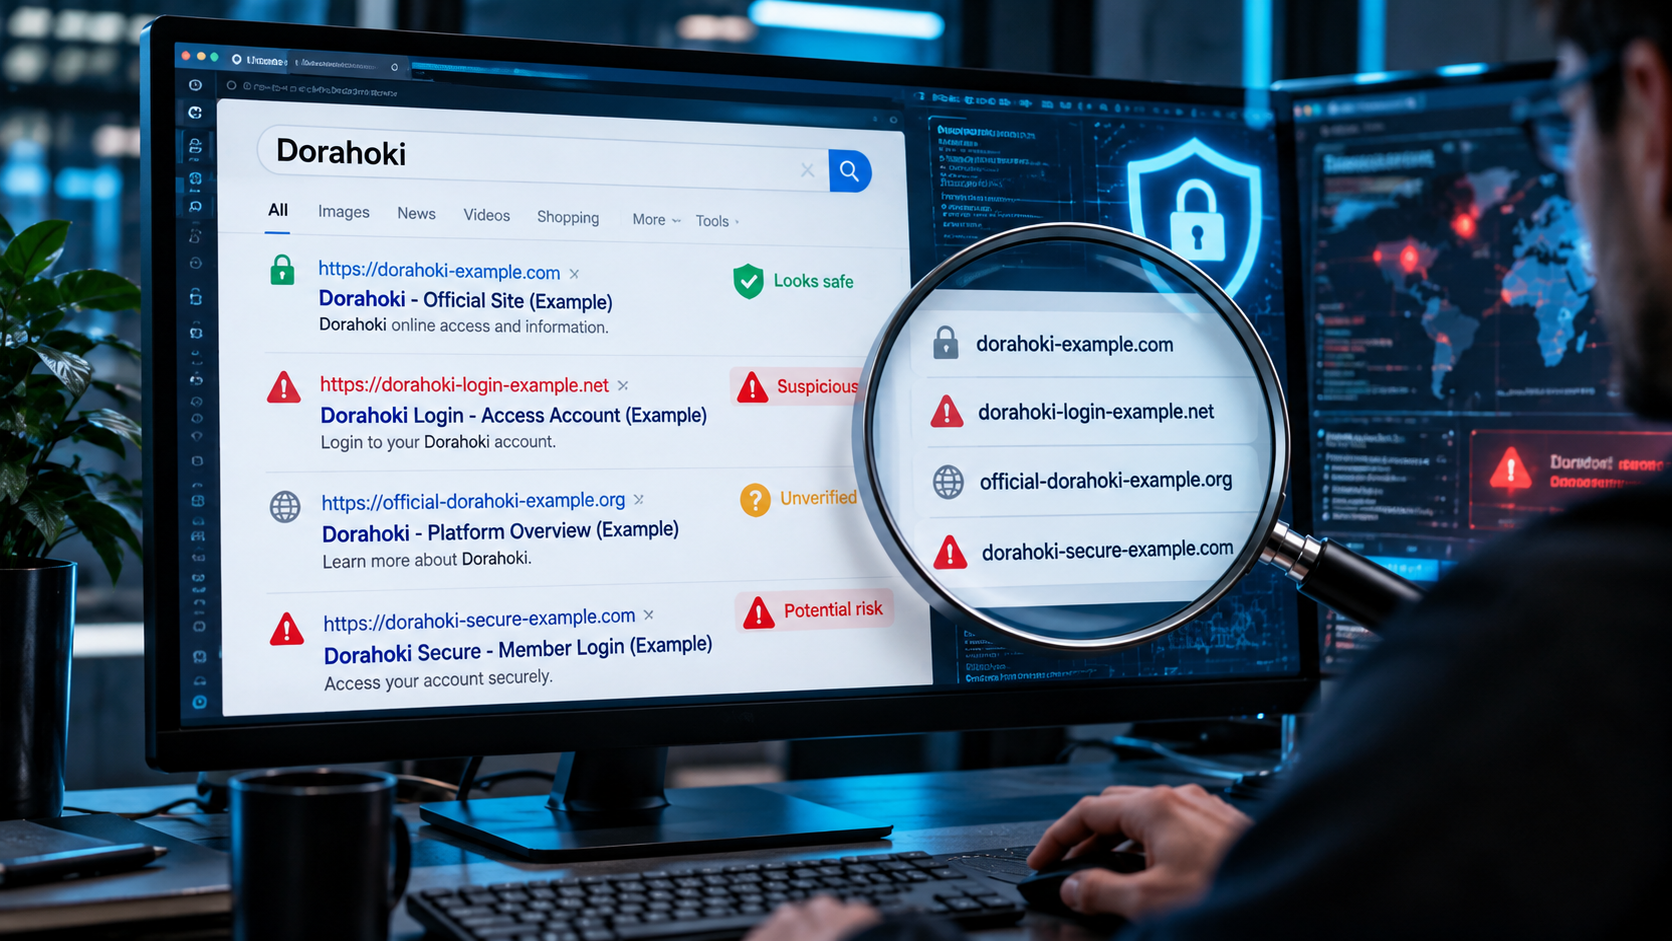
For example, a search result may contain words such as:
Those labels are not proof of ownership.
Any website operator can place words such as “official” or “secure” in a title.
Current search results demonstrate this problem particularly clearly for Direkturtoto. Multiple pages and link aggregators use the name, while some specifically advertise login or alternative access links.
That means users can encounter a path resembling:
Search engine → Direkturtoto link → intermediary page → another domain → final page
The final hostname matters more than the branding displayed along the way.
An alternative link is simply another URL used to reach content or a service.
There are legitimate reasons for alternative URLs.
A company might:
Redirects themselves are therefore not evidence of malicious behavior.
Google documents redirects as a normal part of the web. Permanent server-side redirects such as HTTP 301 and 308 are commonly used when content permanently moves, while temporary redirects such as 302 and 307 can be used when a move is temporary.
The security problem begins when users cannot determine who controls the domains involved or why they are being redirected.
Imagine a fictional example.
A user searches for Direkturtoto and clicks:
direkturtoto-example.com
The browser then moves to:
direct-access-example.net
and finally reaches:
account-example.org
Three different domains have now participated in the session.
The user may remember clicking a page labeled “Direkturtoto,” but the login form is actually hosted on account-example.org.
That distinction is critical.
If credentials are entered, they are being sent to the infrastructure serving the final page — not necessarily the domain the user originally clicked.
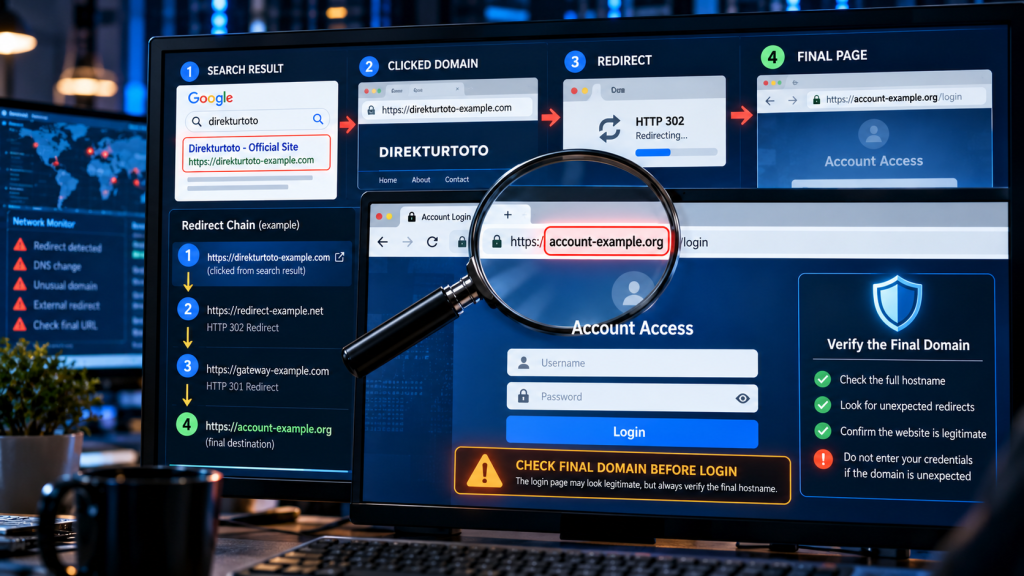
Before entering:
look at the browser address bar again.
Do not assume the hostname remained unchanged after the initial click.
Public technical data provides an especially useful example of why redirect chains deserve attention.
A historical URL scan associated with Direkturtoto-related links recorded a chain passing through numerous different domains before reaching its eventual destination.
The observed path included multiple successive hostname changes.
This finding should be interpreted carefully.
A long redirect chain does not automatically prove malware, phishing or fraud. Redirects can exist for advertising, tracking, domain migration, availability or other reasons.
However, from a security perspective, every additional hostname introduces another point that a user may need to understand.
This makes the Direkturtoto search environment a practical example of an important principle:
The URL you click is not always the URL where you finish.
A redirect occurs when one URL instructs a browser to load another URL.
For example:
example.com/old-page
may return an HTTP response telling the browser to continue to:
example.com/new-page
That is normal web behavior.
Several HTTP status codes can participate in redirects.
| Redirect | General Meaning |
|---|---|
| 301 | Permanently moved |
| 302 | Temporary redirect |
| 303 | See another resource |
| 307 | Temporary redirect |
| 308 | Permanent redirect |
There are also browser-side techniques involving JavaScript or HTML refresh mechanisms.
For legitimate website migrations, Google recommends server-side redirects where possible.
A simple migration might look like:
Old domain → New domain
A redirect chain looks like:
Domain A → Domain B → Domain C → Domain D → Final domain
Long chains are not ideal even for legitimate SEO implementations.
Google specifically recommends avoiding redirect chains during site migrations and keeping them short when they cannot be avoided.
From a cybersecurity perspective, long chains can also make it harder for ordinary users to understand which site they ultimately reached.
Redirects are technology. Their risk depends on how they are used.
Attackers and deceptive campaigns can exploit redirects to hide the ultimate destination of a link.
A user sees a familiar-looking link but ends up somewhere completely different.
An intermediary page can eventually redirect to a login interface designed to capture credentials.
Advertising networks or compromised advertising placements can send visitors through several tracking systems before an unsafe destination appears.
A legitimate website can be hacked and configured to redirect selected visitors elsewhere.
Some systems behave differently depending on:
This can make suspicious behavior difficult to reproduce.
A site owner might see a normal webpage while another visitor receives a redirect.
If you encounter a Direkturtoto-related link, focus on verification rather than branding.
Look at the actual hostname.
A domain containing the word direkturtoto is not automatically controlled by the organization the page claims to represent.
For educational purposes, consider fictional domains such as:
direkturtoto-example.com
direkturtoto-login-example.net
official-direkturtoto-example.org
direkturtoto-secure-example.com
All contain recognizable words.
None becomes authentic merely because of its name.
After clicking a link, check whether the hostname changes.
If it does, ask:
Why did this redirect occur?
A documented migration can have a reasonable explanation.
An unexplained sequence through several unrelated domains deserves more scrutiny.
The final URL is particularly important if the page requests sensitive information.
Do not focus only on the first URL in the chain.
Do not let one website verify itself.
Statements such as:
“Official Direkturtoto”
or:
“Trusted Direkturtoto Link”
are claims, not independent evidence.
Look for consistent domain references from independently verifiable sources.
A common misconception is:
“The browser shows a padlock, therefore this must be the real website.”
That conclusion goes too far.
HTTPS is essential because it protects communication between the browser and the server.
But HTTPS answers a different question:
Is this connection encrypted?
It does not automatically answer:
Does this domain belong to the organization I think it does?
A deceptive website can also use HTTPS.
Therefore, users should check both:
Connection security + destination identity
before submitting sensitive information.
Imagine this fictional sequence:
search.example
↓
direkturtoto-example.com
↓
redirect-example.net
↓
secure-login-example.org
↓
Username + Password form
The most important question at that point is not what logo appears above the form.
It is:
Why is secure-login-example.org requesting the credentials?
Warning signs can include:
No individual sign proves phishing.
Several unexplained signals together justify greater caution.
The terminology can become confusing.
A mirror generally refers to another location hosting the same or similar content.
It may be legitimate when operated by the same organization.
A lookalike domain is designed or happens to resemble another domain.
For example:
direkturt0to-example.com
uses a zero where a user might expect the letter “o.”
Lookalike domains can be used for impersonation and phishing.
This is a broad label for another domain presented as an alternative way to reach a service.
The phrase itself provides no security guarantee.
A compromised domain belongs to a legitimate site owner but has been altered by an unauthorized party.
This last category is particularly important because the domain may have years of legitimate history.
Domain history is useful, but it needs context.
A newly registered domain has little historical reputation.
That can justify additional verification.
However:
New domain ≠ malicious
and:
Old domain ≠ safe
An old domain can:
During current Direkturtoto research, one similarly named domain assessed by third-party reputation services was only a few months old. Different reputation services also reached different levels of concern about it.
That disagreement illustrates why a single automated “trust score” should not be treated as a final verdict.
Use reputation services as signals, not proof.
When a Direkturtoto-related result sends you elsewhere, evaluate the journey systematically.
| Check | Question |
|---|---|
| Initial URL | What domain did I actually click? |
| Redirect | Did the hostname change? |
| Number of hops | Did I pass through several domains? |
| Final URL | Where did I actually land? |
| HTTPS | Is the final connection encrypted? |
| Domain identity | Can ownership be independently verified? |
| Login request | Why is this domain asking for credentials? |
| Downloads | Is the page requesting software installation? |
| Browser warning | Is the browser reporting a security problem? |
| Reputation | Do independent security sources flag the domain? |
The objective is not to find one perfect indicator.
It is to build enough evidence to make an informed security decision.
Cybersecurity researchers can inspect redirects without relying solely on what is visually displayed in the browser.
Useful evidence can include:
Location headers;Public URL-analysis services can also preserve historical scans showing how a URL behaved at a specific point in time.
This historical element matters.
A URL scanned today may behave differently tomorrow.
Therefore, when reporting on suspicious redirects, researchers should specify when the behavior was observed rather than implying it is permanent.
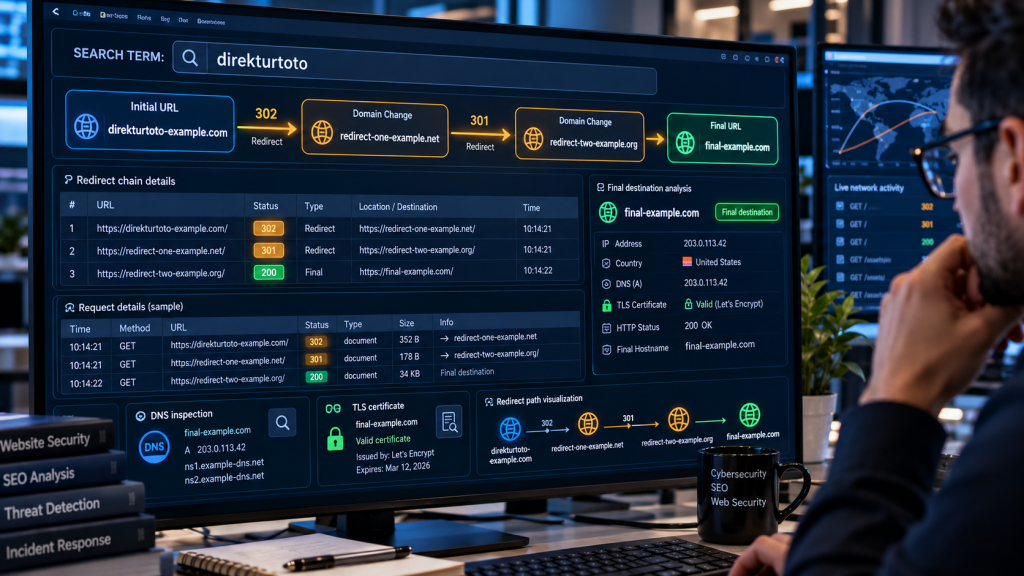
Redirects are not only a security topic.
They are also fundamental to technical SEO.
Google uses redirects to understand when pages or websites have moved.
Permanent redirects can signal that the destination should become canonical, while temporary redirects communicate a different intent.
Poorly implemented chains can create unnecessary complexity.
For legitimate site migrations, Google advises website owners to avoid chains where possible and redirect old URLs directly to their appropriate final destinations.
That produces a cleaner structure:
Old URL → Final URL
instead of:
Old URL → Intermediate 1 → Intermediate 2 → Intermediate 3 → Final URL
This is one area where cybersecurity and technical SEO overlap.
Both benefit from predictable, understandable URL behavior.
It is important not to make an unsupported leap.
The existence of Direkturtoto alternative links or redirect chains does not, by itself, establish malicious activity.
A technically responsible analysis distinguishes observations from conclusions.
A page redirects to another domain.
Several unrelated domains appear in a chain.
The final destination triggers security warnings, imitates another service, requests credentials unexpectedly or delivers malicious software.
This distinction prevents legitimate technical behavior from being mislabeled while still protecting users from genuine risks.
The Direkturtoto case is also relevant to people who operate completely unrelated websites.
Suppose your technology website suddenly starts redirecting visitors to gambling-related domains.
That would be a very different situation.
Potential causes could include:
.htaccess rules;A redirect that you did not configure should be investigated.
If you manage a WordPress site and visitors report unexpected redirects, begin by documenting the behavior.
Record:
Then investigate the WordPress environment.
Look for:
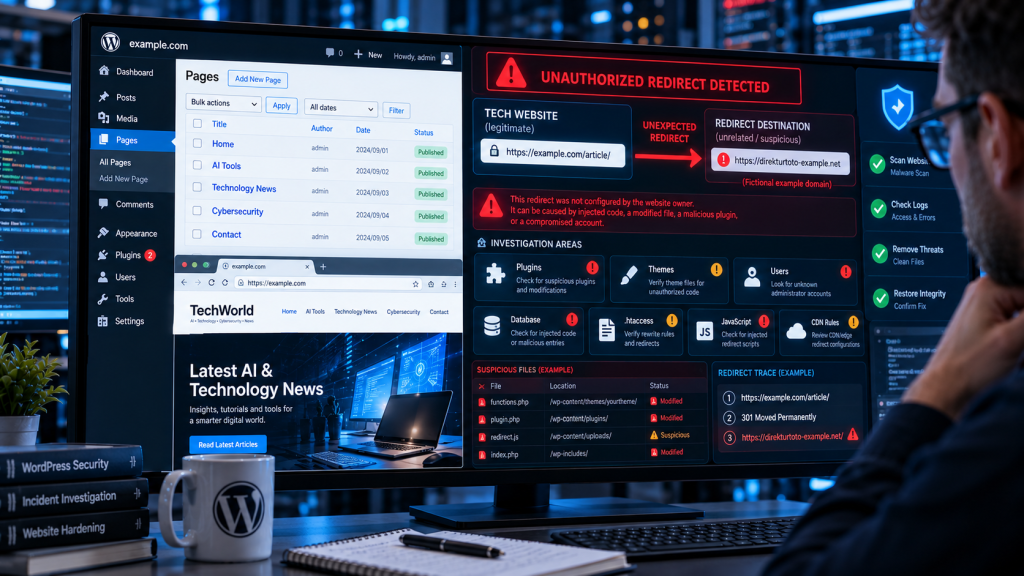
Review WordPress users and confirm every administrator is authorized.
Depending on the server environment, redirects may be configured in:
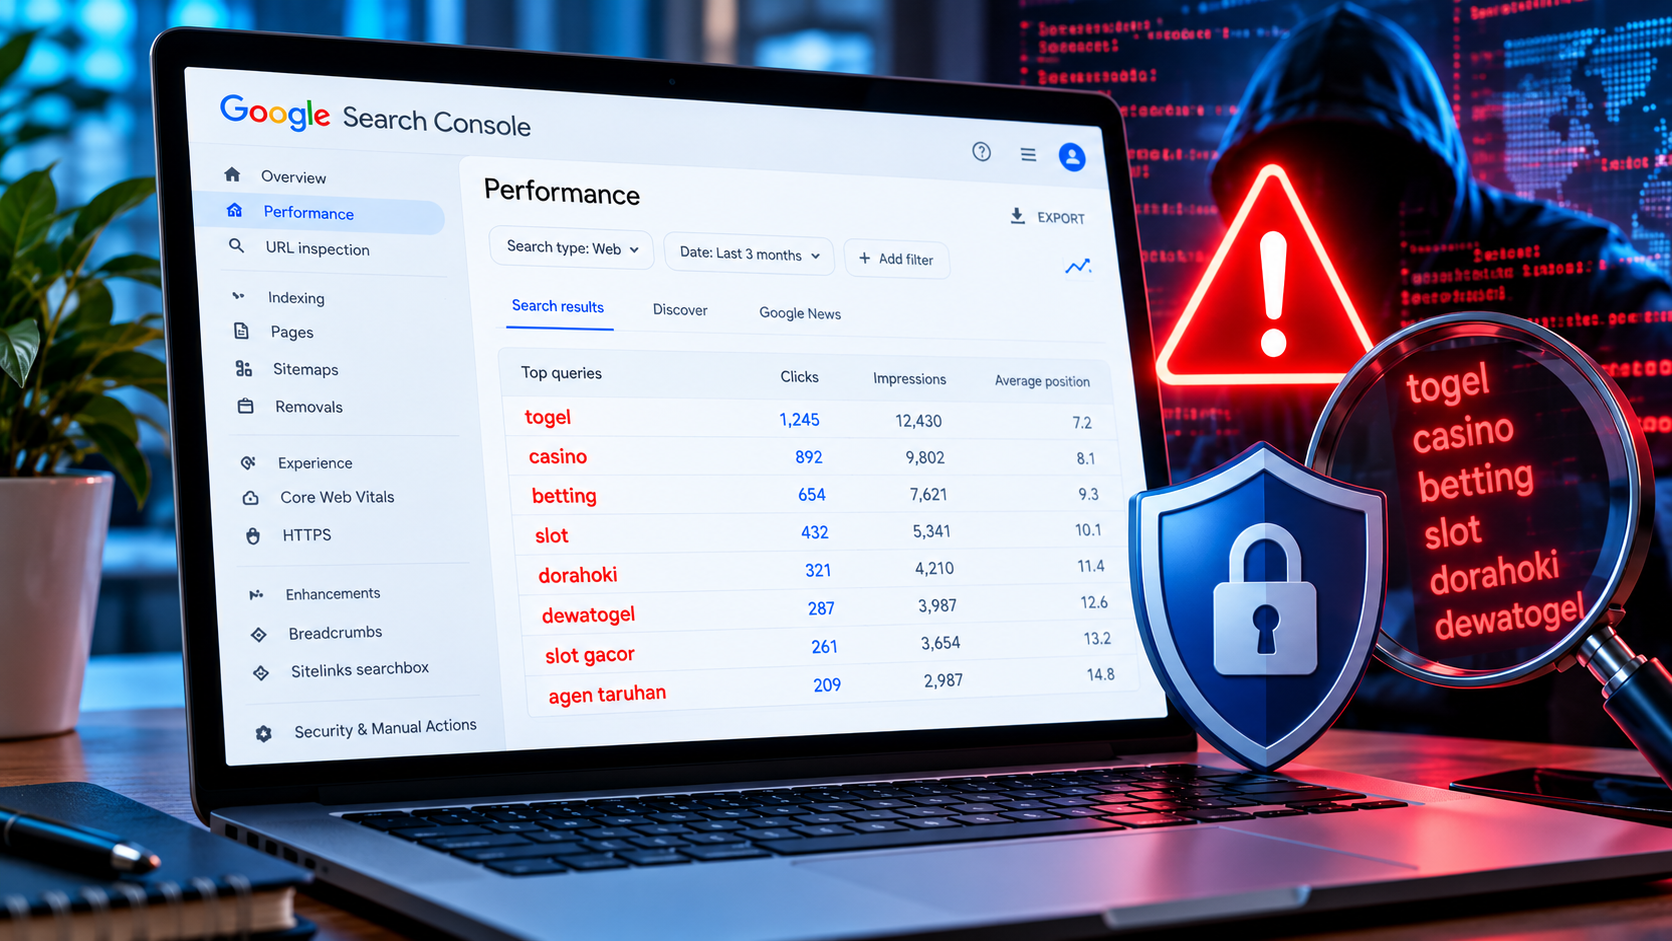
.htaccess;Unexpected gambling URLs or search queries can provide additional evidence of compromise.
For example, an unrelated technology website receiving impressions for direkturtoto alongside unknown URLs would justify further investigation.
The query alone is not proof.
The query → page relationship is the more useful diagnostic signal.
Sensitive information deserves a higher verification threshold.
Before entering a password after any unexpected redirect:
If you already submitted a password to a suspicious page, change that password through a verified destination.
If the password was reused elsewhere, change it there too.
Enable multi-factor authentication when available and review recent account activity.
Search engines actively fight spam and malicious results, but no detection system should be treated as infallible.
Google Safe Browsing, for example, maintains lists of unsafe web resources including phishing, deceptive sites, malware and unwanted software.
Modern browsers can use this intelligence to warn users.
These protections are valuable, but a page that currently displays no warning is not automatically verified as trustworthy.
A new malicious domain may not yet have accumulated enough evidence to trigger reputation systems.
Security works best in layers:
Browser protection + domain verification + independent reputation + careful credential handling
At first glance, Direkturtoto is simply a high-volume navigational search term.
From a cybersecurity perspective, however, its search environment demonstrates several important concepts:
These concepts apply to countless online services.
The larger lesson is that users should follow domain identity, not branding.
A familiar logo can survive every redirect.
The hostname tells you where the browser actually is.
Current search results associate Direkturtoto with online gambling and togel-related content. This article does not evaluate or recommend the gambling service; it examines the cybersecurity implications of the multiple links, domains and redirects associated with the search term.
Search results use “alternative link” to describe other URLs presented as ways to reach Direkturtoto-related content. The phrase does not itself establish that a domain is legitimate or controlled by a particular organization.
Current search results contain several Direkturtoto-related domains, aggregators and alternative-link references. Although one long-standing domain currently presents itself as Direkturtoto, this article does not have sufficient independent ownership evidence to designate a specific login destination as authoritative.
A redirect is not inherently dangerous. Redirects are a normal web technology. Risk increases when unexplained redirects pass through unrelated domains, lead to unexpected login forms, trigger security warnings or produce other suspicious behavior.
Search results show multiple domains and alternative-link references, but that observation alone does not establish why each domain exists or who controls it. Possible explanations for multi-domain structures generally include migrations, mirrors, marketing infrastructure, third-party promotion and other arrangements.
Watch the browser address bar after navigation and identify the final hostname before entering sensitive information. Security researchers can additionally examine HTTP responses and historical URL scans.
No. HTTPS protects the connection between your browser and a server. It does not independently establish that the server belongs to the organization you intended to visit.
A compromised WordPress website can be modified to redirect visitors to unrelated destinations. If you own a non-gambling site and observe unexpected Direkturtoto redirects, investigate plugins, themes, users, files, database content and server/CDN redirect rules.
First determine which URL is receiving impressions. An unrelated query alone does not prove compromise. Unknown pages, injected content or unauthorized redirects provide much stronger reasons for a security investigation.
Direkturtoto demonstrates why users should never evaluate a website solely by the name or logo displayed on the page.
Current search results expose users to multiple domains, alternative-link references and redirect mechanisms. Historical technical evidence also shows that at least one Direkturtoto-related path has passed through a substantial chain of different hostnames.
That does not prove that every redirect or Direkturtoto-branded domain is malicious.
It proves something more useful from a cybersecurity perspective: the first link you click and the final website you reach may be different.
Before entering credentials or personal information, inspect the final hostname, understand unexpected redirects, check independent security signals and avoid treating words such as “official,” “alternative” or “secure” as proof of ownership.
Follow the domain, not the branding.